AI
Explainable AI Meaning: How to Decode Black Box Decisions
Explainable AI transforms opaque algorithmic outputs into readable logic, allowing teams to audit decisions without reverse-engineering the entire model architecture.
Explainable AI transforms opaque algorithmic outputs into readable logic, allowing teams to audit decisions without reverse-engineering the entire model architecture.
HTTP security headers shift defense from server-side code to the client browser, creating a perimeter that blocks many exploits without changing application logic.
Remote browser isolation executes web sessions on a dedicated server, sending only visual pixels to your device, which stops code execution locally.
User provisioning errors create invisible entry points that attackers exploit long after the initial breach detection, often bypassing perimeter defenses entirely.
Vulnerability management shifts security from reactive patching to continuous risk reduction by prioritizing fixes based on actual business impact rather than discovery order.
Synthetic media mimics reality through algorithmic reconstruction, making traditional source verification obsolete and requiring new trust frameworks for digital evidence.
External AI agents bypass standard network controls, creating blind spots where data exfiltration occurs without triggering traditional security alerts.
Business continuity planning shifts the goal from stopping every attack to keeping core services running when defenses fail.
Logic bombs lie dormant in trusted code, waiting for a specific trigger to execute destructive actions without external network connectivity.
Small teams face unique data leakage risks because their limited datasets make each record statistically unique and easier for models to memorize.
Endpoint telemetry reveals hidden process chains that network logs miss, but high-fidelity data creates storage costs and privacy risks that require strict retention policies.
Most teams install SIEM for compliance, but the real value lies in connecting unrelated logs to reveal hidden lateral movement across your network.
Machine learning models fail when training data lacks the specific attack patterns they face in production, creating blind spots that rule-based systems miss entirely.
Most data leaks occur not through model theft but via unfiltered input prompts that bypass application-layer security checks and expose context windows to external processing.
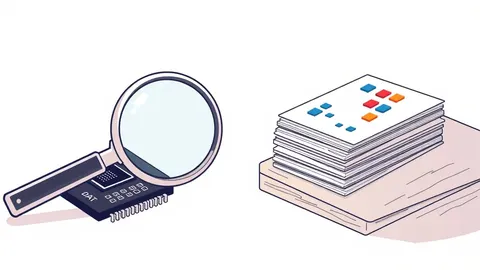
YARA inspects static binary structures while Sigma analyzes structured event logs, creating a complementary detection layer that covers both file-based and behavioral threats.
Machine learning amplifies existing data flaws, turning minor noise into catastrophic false positives if you ignore model drift and feedback loops.
The deep web is not a hidden criminal network but a vast collection of unindexed data that requires specific protocols to access and analyze effectively.
Attackers exploit urgency to bypass rational thought, making the absence of a valid support ticket the most reliable indicator of a fraud attempt.
Archives preserve history with minimal access while backups ensure immediate recovery from deletion or corruption, serving two distinct operational goals.
You can structure a resilient response workflow using standard frameworks and delegated tasks without hiring a dedicated security staff.
Automated response platforms often fail not because of bad code, but because they automate the wrong manual steps without first standardizing the underlying workflow.
Models optimize for statistical patterns, not truth, creating blind spots that attackers exploit through data poisoning and prompt injection.
Fake antivirus uses psychological pressure rather than technical exploits to steal money and install malicious software on your computer.
Unofficial AI tools leave distinct network fingerprints and process anomalies that standard endpoint agents often miss entirely.