
Vulnerabilities
Dependency Confusion Attacks: Risks and Protection for Small Businesses
Attackers exploit the priority rules of package managers to inject malicious code into internal systems without needing external access or credentials.
Vulnerabilities coverage from Sandbox Gazette holds 39 articles, 15 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include OWASP Top Ten and FIRST: Common Vulnerability Scoring System.
Attackers exploit the priority rules of package managers to inject malicious code into internal systems without needing external access or credentials.

Cache poisoning often hides in standard 200 OK responses, making it invisible to traditional error-monitoring tools that only watch for failures.

A critical input validation flaw in Adobe Experience Manager lets privileged attackers execute code without any user interaction.
Coordinated vulnerability disclosure turns chaotic researcher reports into predictable risk inputs for your patch management workflows.
Dynamic application security testing reveals live runtime flaws that static analysis misses, but it requires a working application and careful configuration to avoid false positives.
A critical authorization flaw in Adobe Experience Manager enables remote code execution without user interaction, affecting multiple supported versions.
Prototype pollution allows attackers to inject properties into base objects, bypassing security controls and altering application logic without direct code execution.
A critical authorization flaw in Adobe ColdFusion 2023 and 2025 permits arbitrary code execution without user interaction.
A critical input validation flaw in Adobe Experience Manager 6.5 allows remote code execution without user interaction, posing severe risks to affected systems.
Unauthenticated attackers can write arbitrary files to Risesoft-y9 systems via a high-severity path traversal flaw in versions 9.6.5 through 9.6.11.
Small teams often expose their code repositories to public internet attacks because they treat internal tools as inherently safe from external scrutiny.
Open redirects often bypass web application firewalls because the traffic appears legitimate, requiring specific host-level filtering to stop the abuse chain.
Attackers can run server commands in GPT-SoVITS by manipulating output folder paths in the UVR5 module, posing a severe risk to unpatched installations.
A critical flaw in Wukong_HRM lets attackers bypass authentication entirely, gaining full control over employee data and HR records without credentials.
Attackers are targeting a maximum-severity server-side request forgery flaw in SonicWall SMA 1000 security management appliances.
IBM Db2 Mirror for i versions 7.4 through 7.6 face a critical flaw where authenticated users can bypass validation to run code.
Wordfence researchers found a heap buffer overflow in Ghostscript that allows remote code execution via malicious PDF files.
CERT/CC advisory details multiple vulnerabilities in Thelia 2.6.0 and 2.6.1 that enable remote code execution and other serious risks for e-commerce platforms.
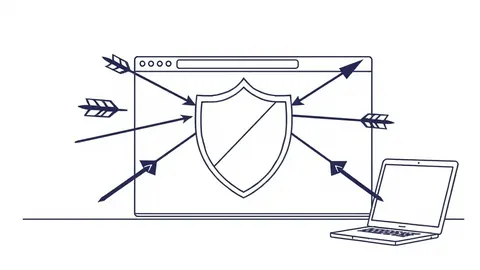
HTTP security headers shift defense from server-side code to the client browser, creating a perimeter that blocks many exploits without changing application logic.
Threat groups like Qilin and Settra are exploiting a Palo Alto authentication bypass to create stealthy, unauthorized remote access sessions.
A critical flaw in Booster for WooCommerce allows attackers to execute code without logging in, posing a severe risk to online stores.
Researchers disclose a chain of flaws allowing remote code execution without credentials, noting that vendor patching complicates remediation efforts.
Vulnerability management shifts security from reactive patching to continuous risk reduction by prioritizing fixes based on actual business impact rather than discovery order.
AWS security bulletins report a local privilege escalation issue involving ESP-in-TCP protocols within the Linux Kernel, requiring immediate attention from IT teams.